

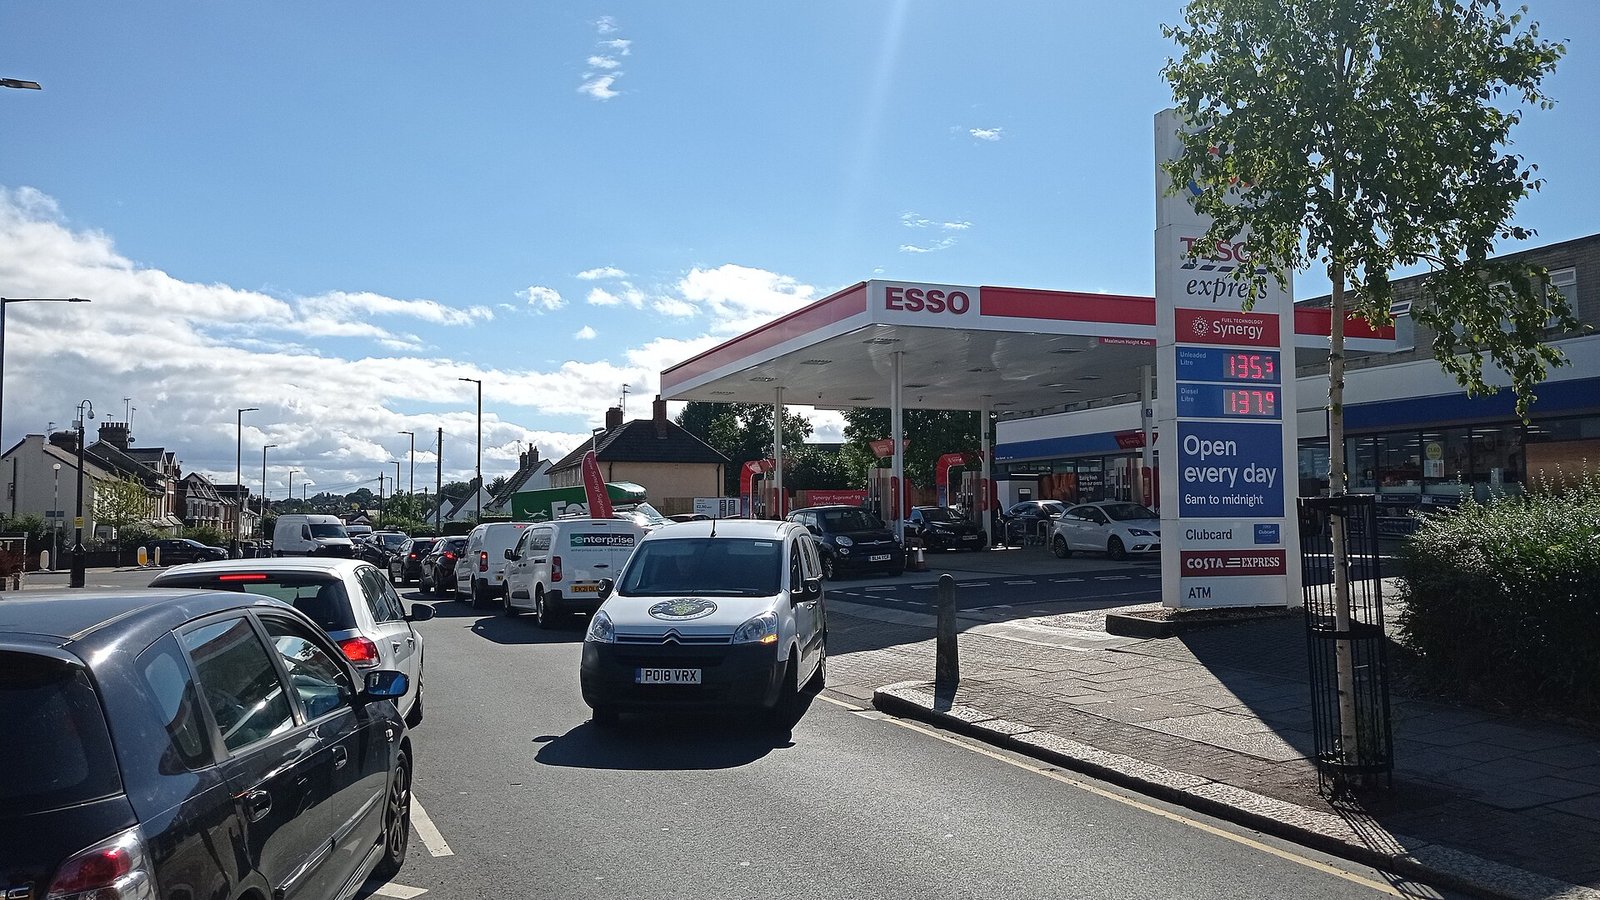
The largest fuel pipeline in the US was shut down by a cyberattack and petrol stations ran dry. Through the Colonial Pipeline crisis, the author reflects on the fragility of critical infrastructure.
Recently the “Colonial Pipeline Company”, one of America’s largest fuel distributors, was hacked. The pipeline carrying about half of the petrol, diesel and jet fuel needed by the country’s east coast, from Texas to New York, suddenly came under cyberattack and the country was in shock. The government, declaring a regional emergency, issued an “all-hands-on-deck” call so as not to leave citizens without petrol. In other words, “anyone with a conscience, come and help.” Strict fuel transport rules were immediately relaxed and fuel was allowed to be carried by tanker on the motorways. Unfortunately this wheel of goodwill could not be turned with fuel carried by road, and the public got its share of the crisis, which lasted about three days.
Because of this cyberattack, which lasted minutes, fuel prices in America suddenly rose. After the company announced that it needed several days to recover, panicked citizens flocked to petrol stations and tried to buy more fuel than they needed. Fuel prices, reaching their highest since 2014, affected a broad section of the public, from motorists to airlines.
The attack is regarded as one of the most serious cyberattacks the US has suffered so far. It is a type of attack known in the cyber world as a “ransomware” attack. It is carried out with ransomware. Malicious software is used that blocks users’ access to files. Almost a quarter of today’s cyberattacks are attacks of this kind.
So how exactly did this incident happen?
First the company’s system was infiltrated and its database seized. All the data was transferred to another hard disk. Then access to all the files was blocked with a password. Suddenly the company could not access its own data. The hackers told the company they would give the password to the database only after a ransom was paid. While waiting for the company’s decision on the ransom, they threatened, with a mocking smile, that confidential financial data would gradually be leaked to the market.
In fact the company’s decision had long been made. They had no answer to such an organised attack. But they did have plenty of money. Although the FBI said “Don’t pay ransoms, increase your cybersecurity”, the company believed it had no choice but to pay the money demanded at once. In the end the ransom was paid. In return for a “Bitcoin ransom” worth about 4.4 million dollars, the oil flow could be restored.
Yet the money that should have been spent to keep the company’s security systems up to date would not have amounted to even half the ransom paid. If they had believed a little in cybersecurity, all this stress would not have been necessary.
During the process, the FBI pointed to the hacker group called “DarkSide”. Of Eastern European origin, DarkSide is a new and different hacker group famous for ransomware attacks. They try to cultivate the image of being the Robin Hood of the cybercrime world. It is even known that they donate to charities. They also stay away from hospitals, state institutions and schools: “We are well-intentioned, we don’t mess with people’s welfare and health. We have nothing to do with politics or geopolitics either. Our business is purely emotional”, they say. Their targets are generally victims with money. The group, which most recently attacked Toshiba, never admits to any connection with the Russian government, but does not deny either that the Russian government turns a blind eye to its presence in the country as long as it attacks Russia’s adversaries.
It is also a fact that there are those with worse intentions than them. For example, in 2020, as a result of a cyberattack on Düsseldorf University Hospital, a patient in an ambulance was redirected to another hospital far away and, sadly, could not be saved.
President Biden said they did not hold Russia responsible for the attack but expected concrete steps against this hacker group: “Everyone must act against illegal activities in their own house”, he said.
Cybersecurity is one of the most problematic areas of information technology today. While security does not require huge budgets, as the examples we have mentioned show, the material damage after an attack can unfortunately be very debilitating. Not only companies but also state institutions must be prepared for cybersecurity threats.
The inability of public institutions and organisations to withstand cyberattacks leads to citizens’ information being seized and confidence in the state being shaken. Such attacks, which can happen in an instant even in the US, which devotes great resources to cybersecurity investment, also point to the need for digital transformation in every institution and every business.
So do you think Turkey stands in the right place on this?
Monthly · free
Compass of the Month
PUGAT’s monthly newsletter.
Read next


What is PUGAT? A non-profit community publishing independent analysis from Europe on security, migration and society in Turkish, German and English.
Go to the homepage
